
Author
No results available
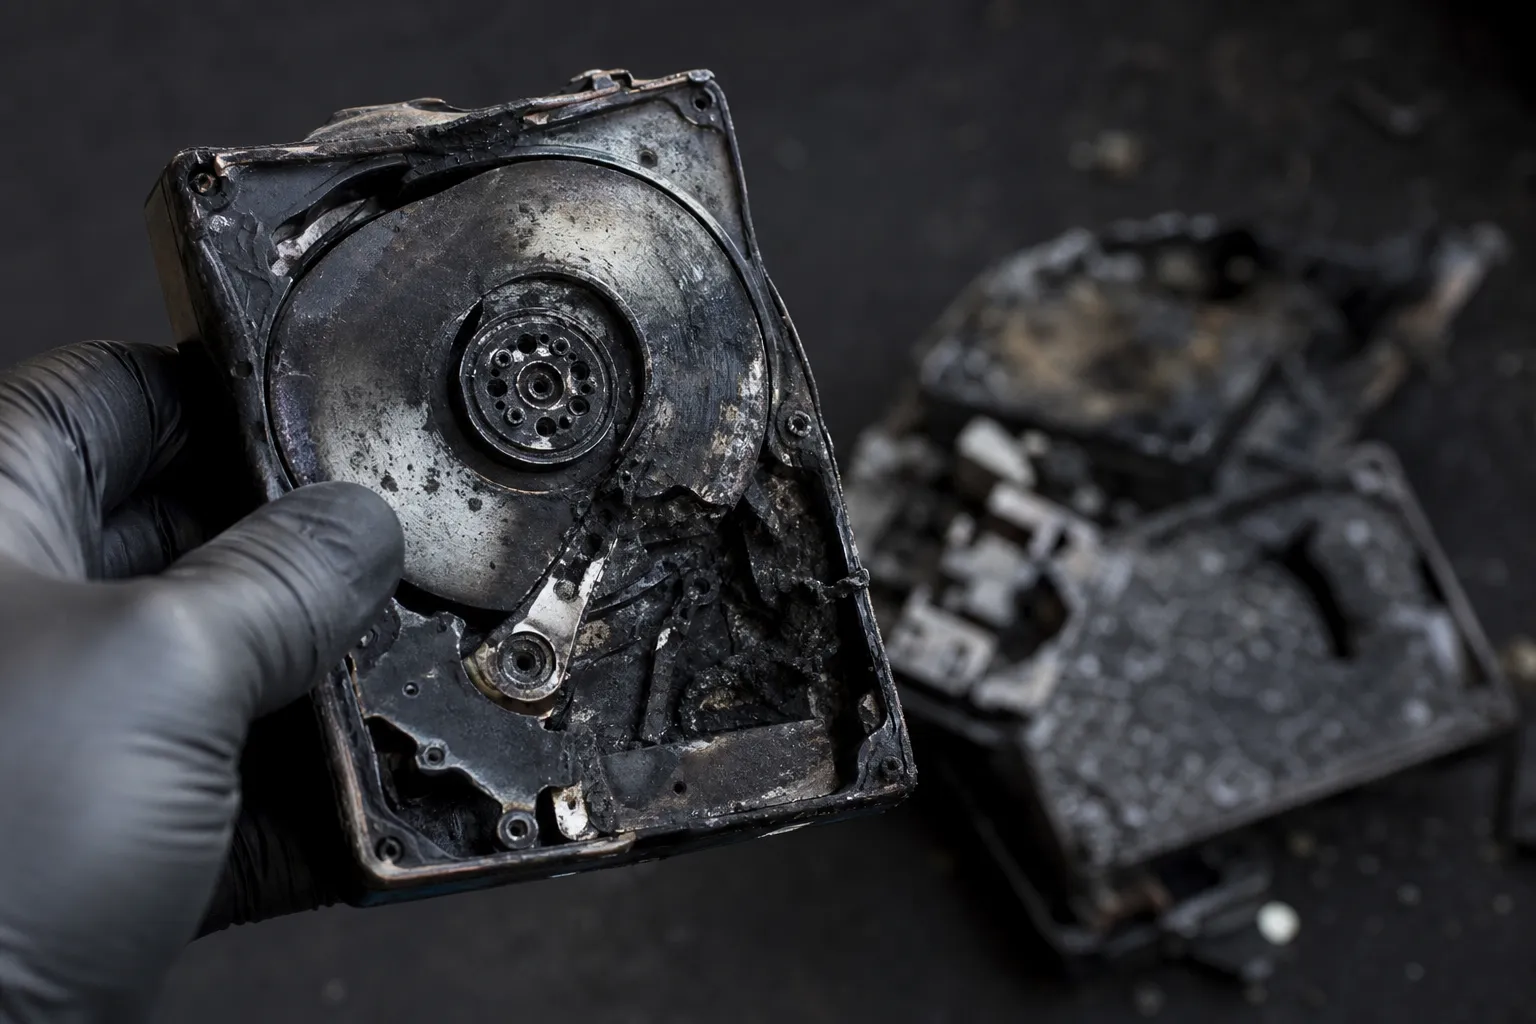
Dealing with a data breach discovered during due diligence of a fintech target is one of the most destabilising moments in an Indian M&A process. A fintech acquisition already sits at the intersection of sensitive personal data, regulated financial infrastructure and systemic trust, so when forensic logs, an internal audit or a late disclosure reveal that customer records have been compromised, the entire deal thesis can shift overnight. In 2026, with the Digital Personal Data Protection (DPDP) Act, 2023 framework maturing alongside long-standing CERT‑In, RBI and SEBI incident-reporting obligations, buyers and sellers face overlapping compliance duties that must be reconciled before anyone signs.
This guide sets out the immediate response, the Indian legal framework, forensic expectations, and the negotiation and deal-structuring tools you can deploy to close safely or walk away cleanly.
Who this guide is for: buyers, sellers, in-house counsel and transaction counsel in fintech acquisitions in India. It covers immediate incident response during due diligence, mandatory Indian reporting obligations under the DPDP Act and sectoral rules, forensic scope, how to allocate liabilities in the share purchase agreement, escrow and price-adjustment options, and sample clause language to manage regulatory and commercial risk.
When a data breach surfaces mid-diligence in a fintech deal, the buyer is confronting more than a technical defect. Fintech targets typically hold payment credentials, KYC documentation, transaction histories and other categories of personal data whose exposure can trigger regulatory penalties, mass data-principal grievances, customer churn and reputational damage that erodes the very franchise being purchased. The breach may also indicate deeper, systemic governance failures that make future incidents more likely.
The strategic choices available to a buyer are stark: walk away, suspend the process pending investigation, or renegotiate price and risk allocation. Dealing with a data breach discovered during due diligence therefore demands a coordinated legal, technical and commercial response within hours, not weeks. The quality of that early response frequently determines whether the transaction survives at all, and on what terms.
Breaches tend to come to light through a handful of routes during diligence:
Whatever the route, treat the discovery as live and ongoing until forensics confirm otherwise.
The early hours matter disproportionately. The twin priorities are containment of the live risk and preservation of evidence, carried out in a way that protects legal privilege and respects the confidentiality controls that govern the diligence process. Both buyer and seller have an interest in a disciplined response: the seller to limit liability and maintain deal value, the buyer to quantify exposure accurately before committing capital.
Recommended actors include the target’s CISO, an external forensic firm, and transaction counsel coordinating the legal and regulatory response. Keep the circle small and documented.
A breach discovered inside a diligence process raises delicate information-handling questions. The non-disclosure agreement and data-room protocols govern how breach materials may be reviewed, copied and shared. Buyers should insist that forensic findings are made available under controlled room conditions rather than circulated freely, and sellers should resist uncontrolled distribution that could itself become a secondary data incident. Document handling, access logging and segregation of highly sensitive material are essential so that the investigation into one breach does not create another.
India’s breach-response landscape is layered. A single incident at a fintech target can simultaneously engage the DPDP Act, CERT‑In’s technical reporting regime, and sector-specific directions issued by the RBI, SEBI or payment-system rules. Dealing with a data breach discovered during due diligence competently means mapping every applicable obligation and identifying who is accountable for each notification. Getting this wrong exposes the target, and potentially the buyer post-closing, to penalties and enforcement.
The Digital Personal Data Protection Act, 2023, published in the Gazette of India, establishes obligations for data fiduciaries, entities that determine the purposes and means of processing personal data. Where a personal data breach occurs, the Act contemplates intimation to the Data Protection Board of India and to affected data principals, with the specifics governed by the Act and its implementing rules. Because the target in a fintech deal is almost always processing large volumes of personal data, buyers must verify that any historic breach was handled consistently with these duties, including whether required notifications were made, when, and to whom.
For the precise statutory text, thresholds and timelines, counsel should work from the Gazette publication of the DPDP Act and its current rules rather than secondary summaries, and should confirm the extent to which the Act’s operative provisions and rules are in force at the time of the transaction.
Undisclosed or mishandled notifications are a serious red flag. They can indicate not only a compliance gap but an attempt to conceal the incident’s scope, which materially affects representations given by the seller.
Separately from the DPDP regime, the Indian Computer Emergency Response Team (CERT‑In), operating under the Information Technology Act, 2000 framework, maintains a technical cyber-incident reporting regime that applies broadly to entities operating digital infrastructure in India. CERT‑In’s directions require reporting of specified cyber incidents within the timelines and in the manner it prescribes, and set expectations for logging and record retention. Fintech targets typically fall within this scope. Buyers should confirm whether CERT‑In was notified in accordance with the applicable directions and whether the target maintained the logs and records that CERT‑In’s directions require.
Where the target is regulated by the Reserve Bank of India, as a bank, NBFC or payment system operator, RBI directions on cybersecurity and cyber-incident reporting impose their own notification duties and controls. If the target is a listed entity or a SEBI-regulated market participant, SEBI’s cybersecurity and cyber-resilience framework and incident-reporting expectations also apply. And where the target participates in payment systems operated by the National Payments Corporation of India (NPCI), additional NPCI rules and controls may be triggered. These sectoral obligations run in parallel with, not instead of, DPDP and CERT‑In duties, so a single breach may require multiple simultaneous reports to different regulators on different timelines.
Depending on the facts, a breach may also implicate penal provisions relating to unauthorised access, data theft and computer-related offences under the Information Technology Act, 2000 and India’s general criminal law. While the deal team’s focus is commercial, counsel should flag any conduct that could attract criminal liability or law-enforcement involvement, as this affects both disclosure strategy and the seller’s willingness to indemnify.
The forensic report is the factual foundation for every downstream decision, valuation, drafting, escrow sizing and regulatory strategy. A buyer should demand a defined scope rather than accepting a seller-commissioned summary at face value. Core elements to specify in the engagement include the time window under review, the systems and data flows in scope, the investigative methodology, and clear requirements for independence and chain of custody.
Engagement-letter points worth negotiating include confidentiality obligations binding the vendor, deliverable formats (interim and final reports), access to underlying artefacts, and cooperation duties that survive the diligence period. Sample deliverables should cover the attack vector, the categories and volume of data affected, dwell time, whether exfiltration occurred, and the remediation already undertaken.
Forensic reports used in a deal can become evidence in later disputes or regulatory proceedings. To maximise the prospect of privilege protection, the forensic firm should be retained by legal counsel for the purpose of providing legal advice, and the report should be marked and handled accordingly. Legal professional privilege in India is governed by the applicable rules of evidence and depends on the involvement of counsel, so structure the engagement deliberately and limit onward disclosure. The Bar Council of India’s rules on professional conduct are a useful reference point where counsel is directing the investigation.
Many fintech targets store backups or route processing through offshore infrastructure. Any export of breach evidence or affected datasets for forensic analysis must itself comply with applicable data-transfer and localisation rules, including any RBI payment-data storage requirements that may apply to the target. Buyers should confirm where data and backups reside, whether cross-border transfers are permitted, and whether the investigation inadvertently triggers additional transfer obligations. This is a frequently overlooked compliance trap when dealing with a data breach discovered during due diligence.
Once the forensic picture is clear, the breach must be translated into commercial terms. The valuation impact is rarely limited to direct remediation cost. Buyers should model several components:
Where exposure is material and uncertain, buyers increasingly commission independent cyber-risk valuations to anchor price negotiations with defensible numbers.
Certain findings should recalibrate the deal entirely: unreported or late-reported incidents, evidence of concealment, systemic data-governance failures, absence of basic logging or access controls, and recurring incidents across multiple periods. These suggest that the discovered breach is symptomatic rather than isolated, and justify either a significant price reduction or withdrawal.
Once a breach is on the table, the share purchase agreement becomes the primary instrument for allocating risk. Buyers want full disclosure, broad protection and recourse; sellers want finite, quantified exposure. The following components are the main negotiation levers.
Buyers should seek specific, breach-focused representations, including that all security incidents have been fully and accurately disclosed, that there are no undisclosed breaches, and that the target has complied with the DPDP Act, CERT‑In requirements and applicable sectoral regulations. A representation confirming the accuracy of the forensic disclosures is particularly valuable, because it converts the factual record into a contractual promise with recourse attached.
Where a known breach exists, a bespoke indemnity, separate from general warranty cover, is standard. Key negotiation points include the breadth of covered losses (remediation, fines, third-party claims, defence costs), caps and baskets, who controls the defence and settlement of claims, and subrogation rights where insurance may respond. Buyers typically press for an uncapped or higher-capped special indemnity for the identified breach, reflecting its known and quantifiable nature.
Data-related representations warrant longer survival than general commercial warranties because breaches often surface well after closing. Indian market practice commonly provides extended survival for data and tax representations, tailored to the risk profile and the practical enforceability of claims within the relevant limitation periods. Counsel should align the contractual survival period with the limitation framework so that the buyer’s remedy remains enforceable throughout.
The following are illustrative drafting candidates. They are sample text, adapt with counsel and must be reviewed against the current DPDP Act, rules and sectoral circulars before use.
When the parties decide to proceed despite a known breach, the structure must ring-fence the residual risk. Escrows and holdbacks are the workhorses here. A time-limited escrow retains part of the purchase price to satisfy breach-related claims, with release conditioned on either the passage of a defined survival period or the completion of specified remediation milestones. Stair-step releases, returning portions of the escrow as milestones are verified, balance the seller’s cashflow concerns against the buyer’s need for security.
Cyber insurance adds a further layer. Buyers should require representations confirming the existence, scope and currency of the target’s cyber policy, confirm that cover is assignable or survives the change of control, and coordinate subrogation and recovery rights so that insurance proceeds and contractual indemnities do not produce double recovery or gaps.
Operational remediation clauses allow closing to proceed while the fix continues. Milestones should be objective and testable, for example, completion of an independent re-assessment, confirmation that notification obligations have been discharged, and verification that affected systems have been patched and monitored for a defined clean period. Tie each escrow tranche to a specific, auditable milestone to avoid disputes on release.
Consider a fintech acquisition valued at ₹500 crore where diligence reveals a breach with estimated remediation and exposure of ₹40 crore. A buyer taking an aggressive stance might demand a ₹60 crore escrow (covering estimated cost plus a contingency buffer), a special uncapped indemnity for the identified breach, and a price reduction for known remediation already quantified. A seller seeking to limit exposure might counter with a ₹25 crore escrow releasing over 18 months, an indemnity capped at the escrow amount, and insurance recovery as the first port of call.
A common middle ground is a ₹40 crore escrow releasing in tranches against remediation milestones, a special indemnity capped above the escrow for defined categories, and coordinated insurance recovery, figures illustrative only.
Closing is not the end of the breach workstream. The SPA should commit the parties to a documented post-closing remediation plan with acceptance testing, grant the buyer audit rights over remediation progress, and set clear escrow draw procedures. Where notifications to regulators were not completed before closing, the agreement must specify who discharges them post-closing and on what timeline, and the seller should remain obliged to provide remediation support and cooperation.
Dealing with a data breach discovered during due diligence ultimately settles into a predictable negotiation. Buyers push for broad reps, special indemnities, larger escrows, longer survival and price reductions. Sellers resist with capped indemnities, shorter survival, insurance-first recovery and milestone-based escrow releases. The common middle ground pairs a right-sized escrow tied to objective milestones with a special indemnity capped above the escrow for defined breach categories, longer survival for data representations, and coordinated insurance recovery. The right balance depends on how quantifiable and contained the breach proves to be once forensics conclude.
| Option | When used | Buyer protection | Seller impact | Likely price effect |
|---|---|---|---|---|
| Walk away / terminate | Material undisclosed breach; intolerable regulatory risk | Full protection (walk away) | Lose deal | High (deal kills value) |
| Fix-before-close | Remediation achievable quickly | Low residual risk at close | Cost and time to seller | Minimal if seller pays |
| Escrow / holdback (time-limited) | Latent liabilities possible | Funds accessible for claims | Funds withheld; cashflow impact | Moderate, reduced upfront price |
| Price adjustment (earnout-style) | Uncertain future impact | Price reduced or contingent | Payment deferred / uncertain | Moderate to high depending on structure |
| Indemnity with cap/basket | Known quantified risk | Contractual recovery (subject to cap/basket) | Liability exposure up to cap | Moderate; cap may be high |
| Insurance-first recovery | If valid cyber policy | Recovery via insurer, subject to policy | May require co-operation | Low immediate cost; longer recovery |
Dealing with a data breach discovered during due diligence of a fintech acquisition in India is a test of speed, discipline and legal craftsmanship. The parties must contain and investigate the incident under privilege, reconcile overlapping DPDP, CERT‑In and sectoral reporting duties, quantify the exposure honestly, and then translate the findings into representations, indemnities, escrows and, where appropriate, price adjustments. Done well, a transaction can survive even a serious breach on terms that fairly allocate risk; done poorly, the buyer inherits liabilities it never priced.
Given the pace of regulatory change and the severity of the obligations involved, every step of dealing with a data breach discovered during due diligence should be reviewed by qualified India corporate and regulatory counsel, and all sample clauses in this guide treated as negotiation starting points to be adapted with professional advice.
This article was produced by Global Law Experts. For specialist advice on this topic, contact Sujata Angadi at Law Veritas West, a member of the Global Law Experts network.
posted 6 minutes ago
posted 26 minutes ago
posted 46 minutes ago
posted 1 hour ago
posted 1 hour ago
posted 2 hours ago
posted 2 hours ago
posted 2 hours ago
posted 3 hours ago
posted 3 hours ago
posted 3 hours ago
posted 3 hours ago
No results available
Find the right Legal Expert for your business

Send welcome message